Shopware 6 Security Plugin
by shopware AG
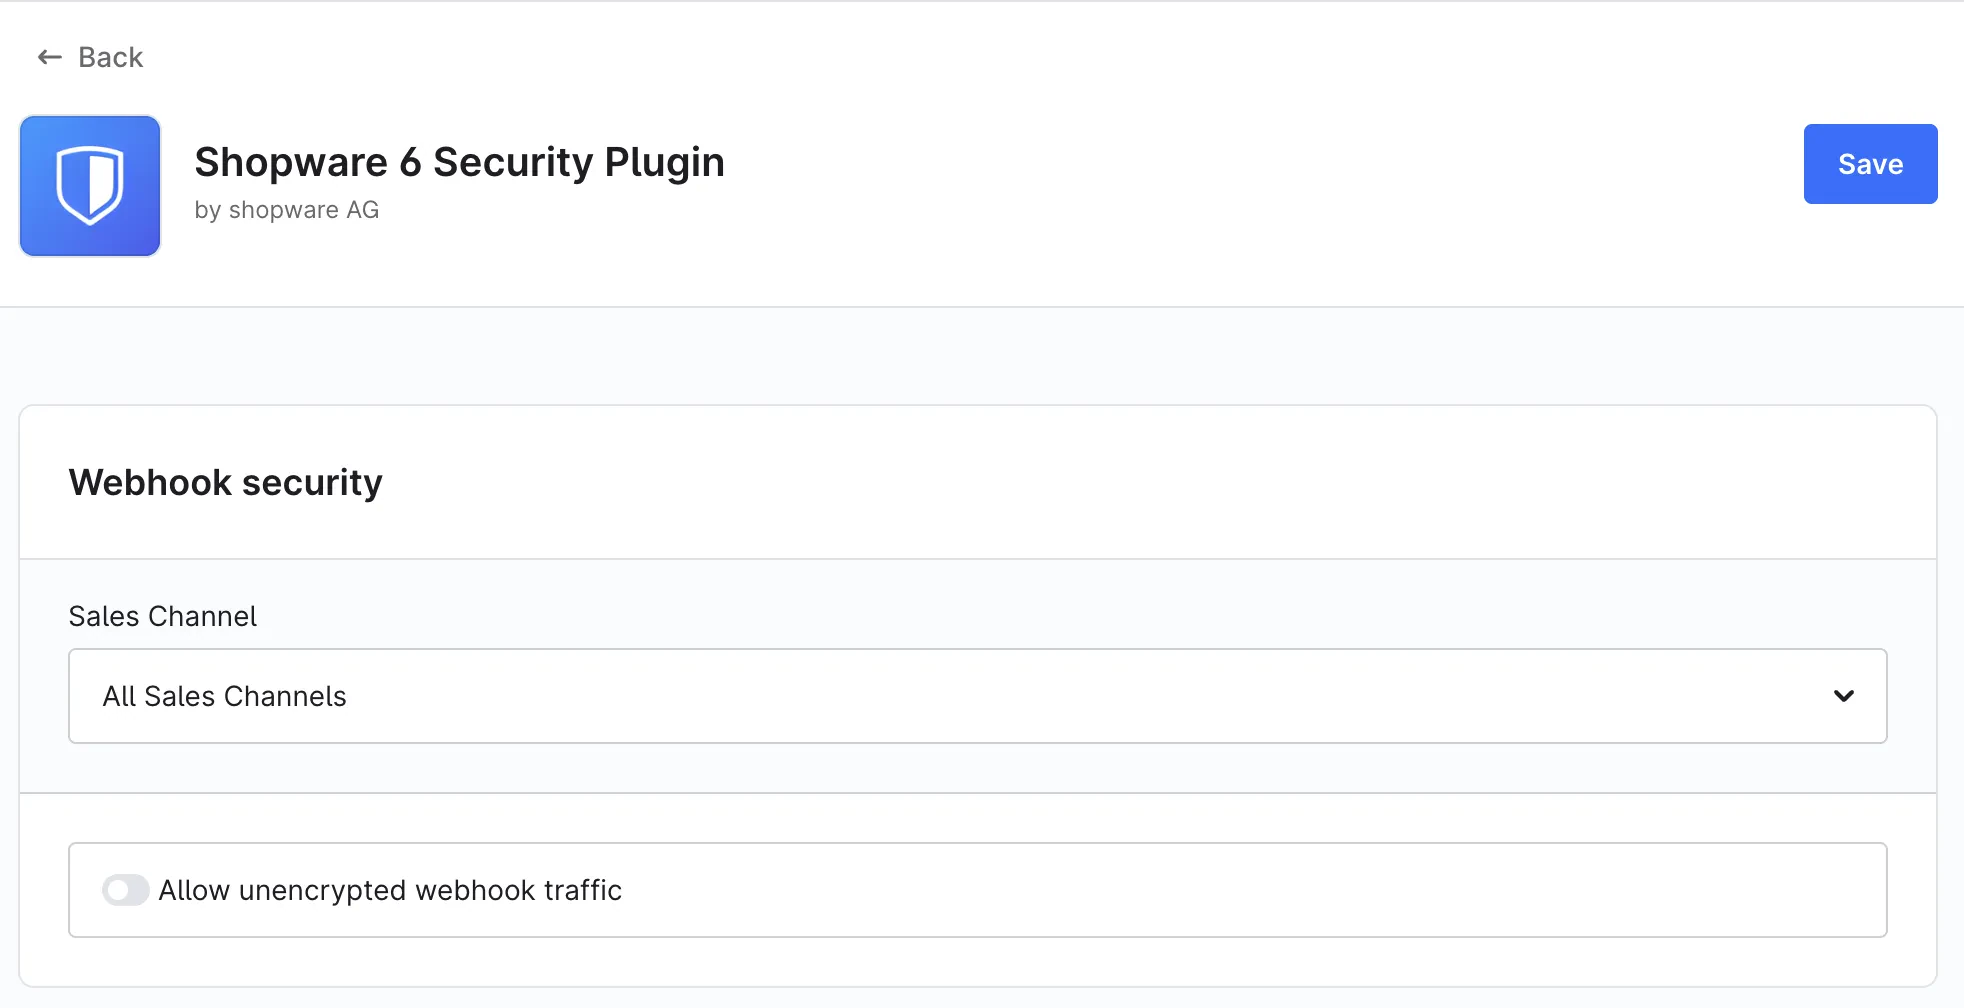
Shopware 6 Security Plugin is developed by Shopware AG and provides security-related fixes for existing Shopware installations. It enables certain known vulnerabilities to be addressed through a plugin update without requiring an immediate full update of the Shopware installation.
The extension is intended for cases where a regular Shopware update first needs to be planned, tested, or coordinated with connected systems. Applicable security fixes are loaded by default once the plugin is activated. A fix is only applied when the installed Shopware version is affected by the related security issue.
Available fixes can be reviewed and managed in the Shopware Administration. Individual fixes can be disabled if they conflict with a customization. The plugin also provides a Composer security advisory check and can display supported advisory-policy entries for composer.json.
Key Features at a Glance
- Delivers security-related fixes through plugin updates.
- Backports security fixes for supported Shopware versions.
- Automatically enables applicable fixes after plugin activation.
- Loads fixes only for Shopware versions affected by the respective issue.
- Provides an overview and management of security fixes in the Shopware Administration.
- Allows individual fixes to be disabled when required.
- Supports checks for Composer security advisories.
- Provides compatible plugin versions for Shopware 6.5, 6.6, and 6.7 according to the Shopware documentation.
Important Notice
This plugin does not replace regular Shopware updates. It is intended as a temporary protection measure until a complete update can be performed. Vulnerabilities in third-party dependencies, such as Symfony or Twig, are not covered by the plugin and require a dependency or Shopware update.
Keep the plugin up to date and apply regular Shopware and dependency updates as soon as possible.
Open Source and License Notice
This plugin is based on the open-source project Shopware 6 Security Plugin by Shopware AG and is distributed through our platform. Unless stated otherwise, this plugin is provided under the terms of the MIT License as declared in the project's composer.json.
Copyright (c) Shopware AG
The software is provided “as is”, without warranty of any kind, to the extent permitted by applicable law. The terms of the MIT License shall prevail. More information about the project can be found here: https://store.shopware.com/en/swag136939272659f/shopware-6-security-plugin.html
Changelogs
4.0.15
Shopware version: 6.717th September 2026 (2 hours ago)
- Added fix for GHSA-mch6-932v-3cm8. Newsletter subscription activation now consistently enforces configured double-opt-in requirements.
- Added fix for GHSA-p589-2ff8-3wfw. Admin API clone operations reject User and Integration records with 403 and reject overwrites of write-protected fields, while retaining copied write-protected fields.
- Added fix for GHSA-2qxr-vvj4-5934. Rejects backticks, question marks, colons, and control characters in aggregation names and range aggregation keys before the SQL query is built.
- Added fix for GHSA-r432-q883-wgvf. Webhook payloads and customer API responses no longer expose sensitive event data, and checkout.customer.deleted requires customer:read.
- Added fix for GHSA-8xfc-pww7-3rm5. The profile update route (PATCH /api/_info/me) now accepts avatarMedia only as an id reference ({"id": ""}).
3.0.19
Shopware version: 6.617th September 2026 (2 hours ago)
- Added fix for GHSA-mch6-932v-3cm8. Newsletter subscription activation now consistently enforces configured double-opt-in requirements.
- Added fix for GHSA-p589-2ff8-3wfw. Admin API clone operations reject User and Integration with 403 and reject protected overwrites while retaining copied protected fields.
- Added fix for GHSA-2qxr-vvj4-5934. Rejects backticks, question marks, colons, and control characters in aggregation names and range aggregation keys before the SQL query is built.
- Added fix for GHSA-r432-q883-wgvf. Webhook payloads and customer API responses no longer expose sensitive event data.
- Added fix for GHSA-8xfc-pww7-3rm5. The profile update route (PATCH /api/_info/me) now accepts avatarMedia only as an id reference ({"id": ""}).
4.0.14
Shopware version: 6.727th August 2026 (3 weeks ago)
- Fixed the Twig callable security patch on Shopware 6.7.8.0–6.7.13.0. SEO URL generation no longer registers core Twig extensions twice.
- Fixed Administration startup on Shopware 6.7. The Security plugin now reads active fixes from the supported Administration context store.
3.0.18
Shopware version: 6.627th August 2026 (3 weeks ago)
- Added fix for GHSA-rrc3-p9vx-5373. Validates webhook and App System targets and pins each connection to its checked DNS address.